Featured YARA rule: Top 10 Ransomware Threats

  • Dec 15, 2023 4:43 PM UTC
  • Dec 19, 2023 5:43 PM UTC
  • 16 comments
  • 3153 views

Rick Vanover
Forum|alt.badge.img+10

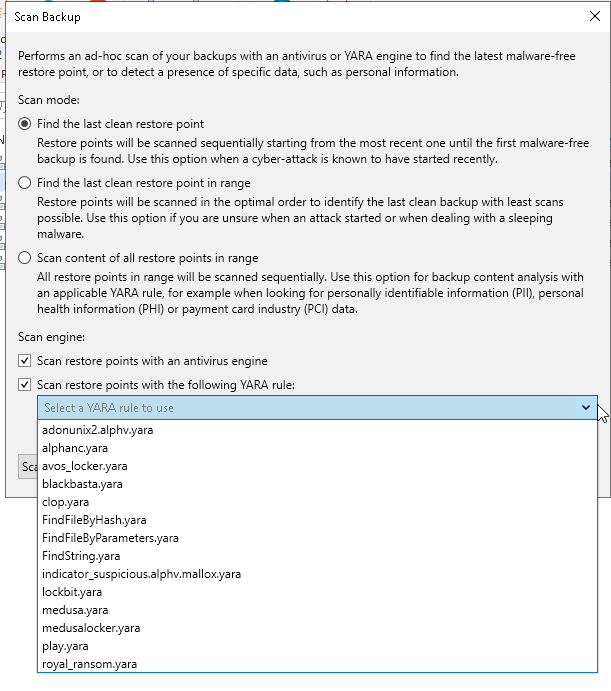
Now that V12.1 is available, I wanted to share with you a featured YARA rule set that can give you on-demand scanning for some top ransomware threats. 

Attached to this post is a file named: Top10RW_YARArules.zip. In this file are YARA rules for some common ransomware threats that have been seen recently:
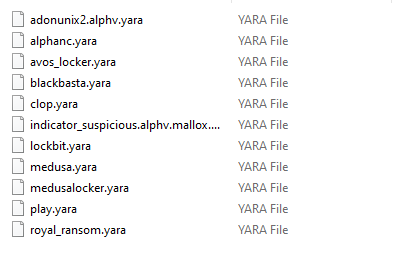
Attribution: This great collection was made by Felix Bilsten. Links: X: Felix Bilstein (@fxb_b) / X (twitter.com), website: Felix Bilstein - project overview (cocacoding.com) and Github: fxb-cocacoding (Felix Bilstein) · GitHub
16 comments

Chris.Childerhose
Forum|alt.badge.img+23

Thanks for sharing these, Rick.  Looking forward to exploring Yara with 12.1.


coolsport00
Forum|alt.badge.img+23
  • Veeam Legend
  • Dec 15, 2023 6:49 PM UTC

Fantastic Rick! Appreciate the share. Will look at this for sure after I get my environment upgraded.


Rick Vanover
Forum|alt.badge.img+10
  • Author
  • RICKATRON
  • Dec 15, 2023 6:51 PM UTC

Cheers, Shane.


JMeixner
Forum|alt.badge.img+18
  • On the path to Greatness
  • Dec 15, 2023 7:31 PM UTC

Thanks Rick, I will try this on Monday 😎👍🏼


BertrandFR
Forum|alt.badge.img+7
  • Influencer
  • Dec 16, 2023 12:00 PM UTC

Thanks for sharing @Rick Vanover , any comments about it @Julien Mousqueton ?


Scott
Forum|alt.badge.img+10
  • Veeam Legend
  • Dec 18, 2023 4:13 PM UTC

This is great. I’ll add it to the lab this week!


JMousqueton
Forum|alt.badge.img+3
  • Comes here often
  • Dec 19, 2023 6:05 PM UTC

@Rick Vanover & @BertrandFR 

Find bellow the golden mine of Yara rules : 

https://yarahq.github.io
 

“YARA Forge specializes in delivering high-quality YARA rule packages for immediate integration into security platforms. This tool automates the sourcing, standardization, and optimization of YARA rules from a variety of public repositories shared by different organizations and individuals. By collating these community-contributed rules, YARA Forge ensures that each package meets rigorous quality standards, offering a diverse and comprehensive rule set.” 


Link State
Forum|alt.badge.img+12
  • Veeam Legend
  • Dec 20, 2023 9:46 AM UTC

Thank you @Rick Vanover  everything seems okay.

uploaded C:\Program Files\Veeam\Backup and Replication\Backup\YaraRules

Launched scan yara medusa no error at the moment.
Thanks for sharing.


Scott
Forum|alt.badge.img+10
  • Veeam Legend
  • Dec 20, 2023 4:41 PM UTC

Tested in my lab and it worked great. (minimal CPU available and a pretty small backup set)

I’m excited to get more into Yara rules and look forward to posting some writeups and new rules for people to try on here. 


  • New Here
  • Jan 4, 2024 11:49 PM UTC

@Rick Vanover & @BertrandFR 

Find bellow the golden mine of Yara rules : 

https://yarahq.github.io
 

“YARA Forge specializes in delivering high-quality YARA rule packages for immediate integration into security platforms. This tool automates the sourcing, standardization, and optimization of YARA rules from a variety of public repositories shared by different organizations and individuals. By collating these community-contributed rules, YARA Forge ensures that each package meets rigorous quality standards, offering a diverse and comprehensive rule set.” 

Trying the core ruleset tonight!


damien commenge
Forum|alt.badge.img+7

Hello,


Thanks for sharing it @Rick Vanover 

I’m sorry but I ‘m not sure to understand really what YARA rules are for ? 

I need to select 1 rule like “test eicar” for VBR to scan file backup and say me yes there is eicar on this file backup ?

I’m sorry I don’t know anything about it but not sure I understand the benefits when I compare to other new 12.1 feature like inline detection (I don’t have to create any rules) or suspicious activity detection ?
Thanks for your explanations :)


  • New Here
  • May 20, 2024 7:43 PM UTC

The yara file adonunix alerts a lot of false positives, primarily it detects windows update packages as threats. Is this supposed to happen, or I should worry about it?


Rick Vanover
Forum|alt.badge.img+10
  • Author
  • RICKATRON
  • May 20, 2024 9:13 PM UTC

The yara file adonunix alerts a lot of false positives, primarily it detects windows update packages as threats. Is this supposed to happen, or I should worry about it?


Hi @mmalarino → Yes, windows update have also hit a lot of false positive for massive encryptions also. We are tuning the logic often. Stay tuned. And welcome to the Veeam community :)


  • New Here
  • May 20, 2024 9:21 PM UTC

@Rick Vanover thanks for the rules and the chance for a test. I'll be looking forward for more info!


Filik
  • New Here
  • Aug 14, 2025 1:51 PM UTC

Thanks Rick, I was looking for something like this.

I went and merged all of the 10 rules from the zip in one single .yar file, so its one entry to select it and wait for the scan outcome.


waqasali
Forum|alt.badge.img+4
  • On the path to Greatness
  • Aug 17, 2025 1:31 PM UTC

Thanks ​@Rick Vanover This is a solid step toward proactive ransomware defense.